
WordPress Compliance Services
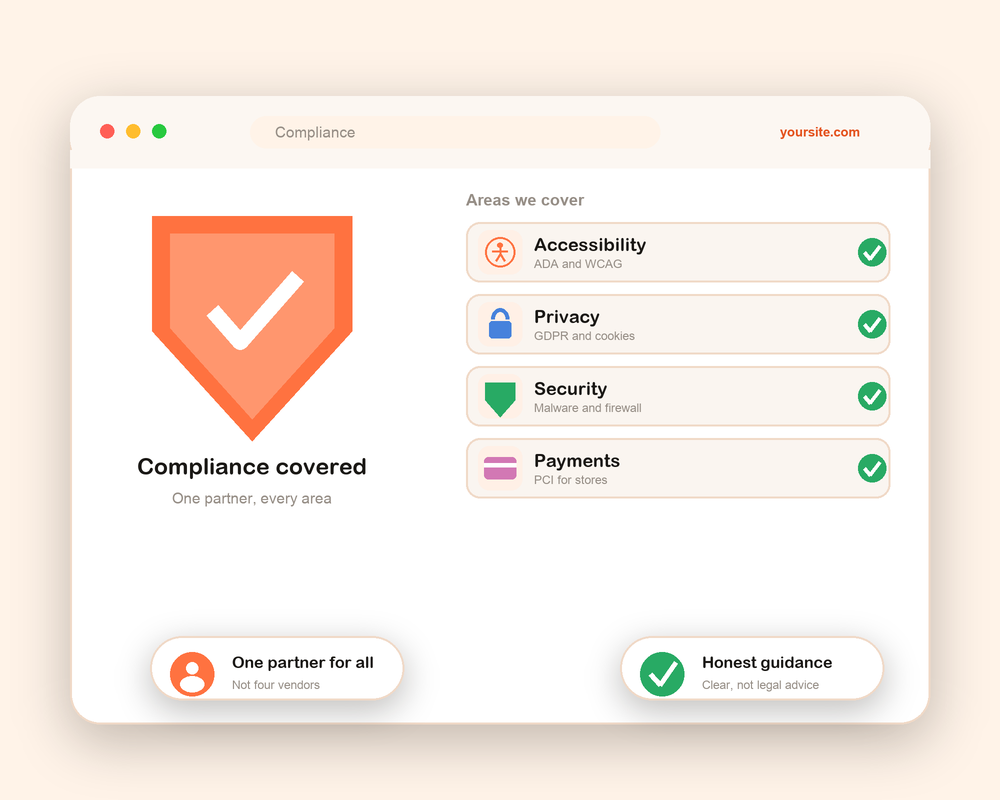
Accessibility, privacy, payments, and security, handled by one team. We help your WordPress site meet the standards that matter, from ADA and WCAG to GDPR and cookie consent to PCI for stores, with honest guidance and real fixes. One partner for the whole picture, not four.
Accessibility
ADA and WCAG
Privacy
GDPR and cookies
Payments
PCI for stores
Security
Protected and monitored


WordPress Website Compliance, Made Clear
Website compliance is a broad term that covers several different rules, and most of them have nothing to do with each other. There is accessibility, which is about people with disabilities being able to use your site. There is privacy, which is about how you handle personal data and cookies under laws like GDPR and CCPA. There is payment security, or PCI, for sites that take card payments. And there is general website security, which underpins all of it.
You do not need to be an expert in any of this. What you need is a clear picture of which rules apply to your site and a team that can handle the WordPress side of each one. That is what we do. This page explains the main areas, helps you work out what applies to you, and links to the deeper pages for each. A quick note up front: this is general information, not legal advice, so for your exact obligations please also speak with a lawyer.
The Compliance Areas We Cover
Each area is its own topic with its own rules. Here is what each one means, and where to go for the detail.
Make your site usable for people with disabilities and meet WCAG, the standard behind ADA. Real fixes, not an overlay widget.
Handle personal data and cookies properly, with real consent that blocks tracking until visitors agree, and clear privacy policies.
A proper consent banner that actually blocks non essential cookies until people opt in, with records kept, not just a notice.
If you take card payments, keep card data off your server with a trusted gateway, and run a secure, updated store.
Malware protection, firewalls, secure logins, and monitoring, the foundation that every other kind of compliance rests on.
Clear privacy, cookie, and terms pages written to match what your site actually does, not a generic template.
Which Rules Apply to Your WordPress Site?
Not every rule applies to every site, and that is the first thing to get clear. If your site is open to the public, accessibility is worth taking seriously, and for public sector sites it is a clear duty. If you collect any personal data or reach visitors in the EU or UK, privacy rules like GDPR come into play, and US state laws like CCPA may apply too. If you take card payments, PCI applies. And security underpins all of it.
Most small business sites need accessibility and privacy handled, and stores need payment security on top. We start by working out exactly what applies to your site, so you are not paying for things you do not need or missing something that matters. Then we handle each area properly on the WordPress side.
How We Handle Compliance
One clear process across every area, so nothing is missed and you always know where you stand.
1
Review
We work out which rules actually apply to your site, so the scope is right from the start.
2
Audit
We check your site against each area that applies, from accessibility to privacy to payment security.
3
Fix by Area
We handle each area properly, with real fixes, the right tools, and clear policies where needed.
4
Document
We document what was done, so you can show your work if a customer, auditor, or regulator ever asks.
5
Maintain
Rules and sites both change. We keep your compliance current as you add content and tools.
You get one team and one plain language summary across every area, instead of chasing separate vendors.
Why Choose Optmistic Technologies
Compliance is an area full of fear selling and false promises. Here is how our honest, practical approach is different.
One partner, every area
Accessibility, privacy, payments, and security under one roof, so nothing falls through the gap between vendors.
Honest, not scaremongering
We give clear guidance and never invent lawsuit numbers or false guarantees to sell you more than you need.
Real fixes
We fix the actual code and setup, not cover issues with a widget that only looks compliant.
We say what applies
We start by working out which rules apply to your site, so you do not pay for things you do not need.
Not legal advice, and we say so
We handle the WordPress side and point you to a lawyer for legal certainty, rather than pretending to be one.
Kept current
Rules and plugins change. We keep your compliance up to date as your site grows.
WordPress and PCI Compliance for Online Stores
If your WordPress site takes card payments, PCI DSS applies. PCI is the payment card industry’s security standard, set by the card brands rather than a government, and it is about keeping cardholder data safe. For most small and medium WooCommerce stores, the practical goal is simple: never let raw card details touch your own server.
The easiest and safest path is to use a trusted payment gateway like Stripe or PayPal, where the customer enters their card on the provider’s secure systems, not yours. Your store never stores or processes raw card numbers, which keeps you in the simplest PCI category and takes most of the burden off you. We set up your WooCommerce checkout with a hosted or tokenised gateway, keep your site, plugins, and server updated and secure, and make sure checkout always runs over HTTPS. For a formal assessment and your exact self assessment level, your payment provider or a qualified assessor can confirm the details.
Honest Guidance, Not Legal Advice
A straight note on how we work. Compliance is an area where a lot of companies sell fear, invent lawsuit statistics, and promise guarantees that no one can honestly make. We do not do that. There is no magic plugin that makes a site compliant, no official certificate for ADA, and no way to promise you will never face a complaint.
What we can do is real and useful: tell you honestly which rules apply to your site, handle the WordPress side of each one properly, document the work, and keep it current. This page and our advice are general information, not legal advice, and we are not lawyers. For your exact legal obligations, we will always recommend you also speak with a qualified professional, and we are happy to work alongside yours.
What a Compliance Project Costs
Because compliance covers several areas, the cost depends entirely on which ones apply to your site and how much work each needs. A small brochure site that only needs accessibility and a privacy policy is very different from a busy store that needs accessibility, privacy, payment security, and ongoing upkeep.
We start with a review to work out what actually applies to you, then audit each relevant area, so you get a clear, fair quote with no hidden costs and nothing you do not need. Tell us about your site and what you are worried about, and we will recommend the right scope.
Get Clear on Your WordPress Compliance
Not sure which rules apply to your site, or whether you are covered? Start with a compliance review. We tell you honestly what applies, handle the WordPress side of each area, and keep it current. One partner for the whole picture.
WordPress Compliance FAQs
What does website compliance mean?
It is a catch all term for several separate rules: accessibility (people with disabilities being able to use your site), privacy (how you handle personal data and cookies, under laws like GDPR and CCPA), payment security or PCI (for card payments), and general website security. They are different topics, and which ones apply depends on your site.
Which compliance rules apply to my WordPress site?
It depends. If your site is public, accessibility matters. If you collect personal data or reach EU or UK visitors, privacy rules apply. If you take card payments, PCI applies. Security applies to everyone. We start by working out exactly which rules apply to your site.
Is my WordPress site ADA compliant?
Almost certainly not by default. WordPress themes, page builders, and content all introduce accessibility issues. Making a site accessible means fixing those issues against the WCAG standard. See our accessibility page for the detail on how we do it.
Do I need to worry about GDPR if I am based in the US?
Possibly. GDPR applies to any site that offers goods or services to people in the EU or UK, or tracks them, wherever the business is based. If you do not target Europe, US state laws like CCPA may apply instead. Our GDPR page explains how we handle it.
What is PCI compliance for a WooCommerce store?
PCI is the card industry’s security standard for sites that take card payments. The practical answer for most stores is to use a trusted gateway like Stripe or PayPal so card details never touch your server, keep your store secure and updated, and run checkout over HTTPS. We set this up for you.
Can one company handle all of my compliance?
Yes, that is the point of this service. Rather than juggling separate vendors for accessibility, privacy, payments, and security, we handle the WordPress side of all of them, with one plain language summary and one point of contact.
Is this legal advice?
No. This page and our guidance are general information, not legal advice, and we are not lawyers. We handle the practical WordPress side of compliance and will always recommend you confirm your exact legal obligations with a qualified professional.